Independent visibility into control testing and policy status, without asking anyone.
The third line should not depend on the second line's spreadsheet. Blueprint+ gives internal audit read access to the same registers, assessments and approval histories the business works in, with an audit log on every action.
Evidence that arrives by email
Audit works from exports the business prepares. By the time fieldwork starts, the export is a snapshot of a moment that has passed.
No trail behind the rating
A control rated effective in a workbook carries no evidence, no reviewer and no date. Audit has to re-perform the test to trust it.
Documents detached from controls
Checking that a policy clause has a working control behind it means two teams and three files.
The same registers the business uses, in real time
An audit role sees the Risk Register, Control Registry, Regulations Library, every policy's version history and every assessment's scores and threads, without the ability to change them. Independence is a permission, not a courtesy.
- Role-based access with read-only audit roles
- Live data, not exports
- Filter by business unit, period or regulator
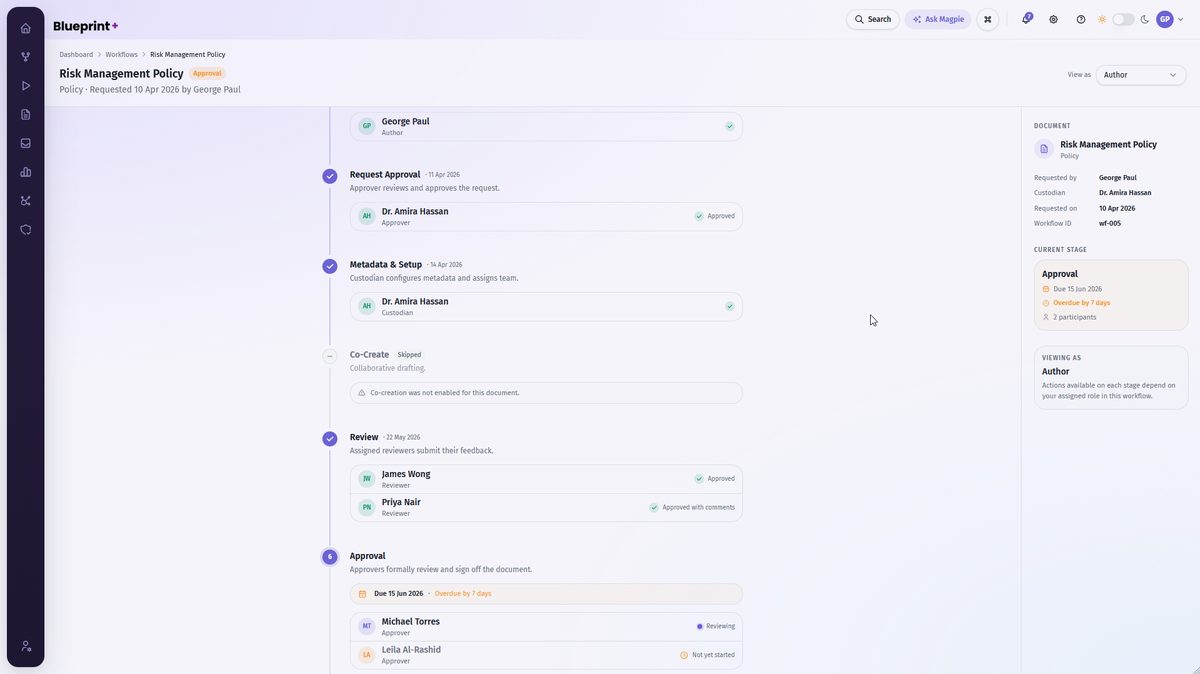
Every rating has a person, a date and evidence behind it
Control ratings, approvals, publications and register changes are logged as they happen, with the actor, the time and the attached evidence. Audit can trace a rating back to the test, the tester and the thread where it was challenged.
- Audit log on every action in the platform
- Evidence attached to control ratings
- Threads preserved with the assessment
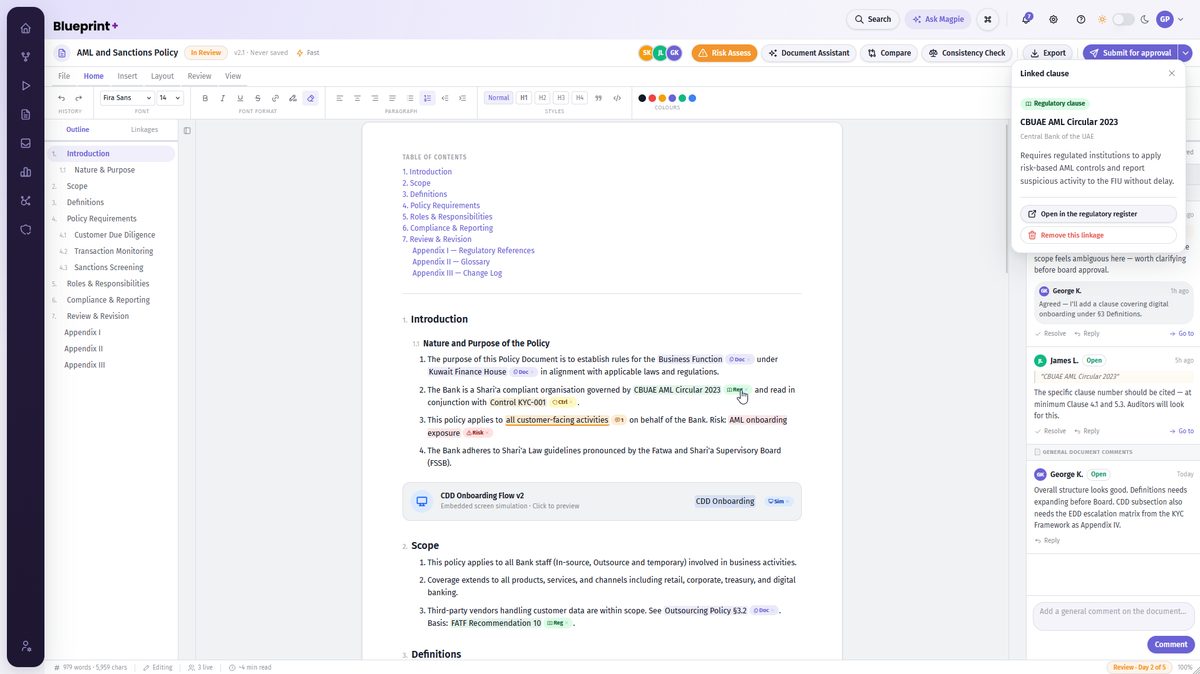
Follow the thread from the clause to the evidence
From any policy clause, open the control that makes it real, the risk it treats and the most recent assessment that tested it. From any control, see the clauses that depend on it. The Impact Analyzer shows what a finding affects, so recommendations land on the right documents.
- Linked items in both directions
- Impact Analyzer for findings and remediation
- Export the trace as working papers
See what the second line sees, as it happens.
Book a demo and bring a recent finding. We will show you the trail from the clause to the test.